


Acronis Advanced Security + EDR
Combine endpoint detection, response and recovery in a single flow.
What does it do?
An endpoint security solution that detects suspicious behaviour on computers and servers, prioritises incidents and, through backup integration, makes post-attack recovery easier.
Which needs does it address?
- Seeing advanced threats that antivirus misses
- Responding to incidents quickly and with the right priorities
- Preserving evidence for post-attack forensic investigation
AI-generated incident summaries
A clear, short explanation for every incident
Incident prioritisation
Ranking that brings critical incidents to the top
Quarantine and isolation
Containing the threat
Forensic backup
Device image for investigation
Patch management
Closing the vulnerabilities used in the attack
Full re-imaging
Rebuilding the affected system from a clean image
- Scenario 1Detecting suspicious PowerShell behaviour and isolating the device
- Scenario 2Reporting the root cause of an attack to management
- Scenario 3Fast recovery from a clean image after an attack
Assessment
We review your current backup, security and licence status.
Deployment
We install agents and policies and carry out the first backups and tests.
Management
Monitoring, incident response and reporting according to your scope.
Security + EDR at a glance
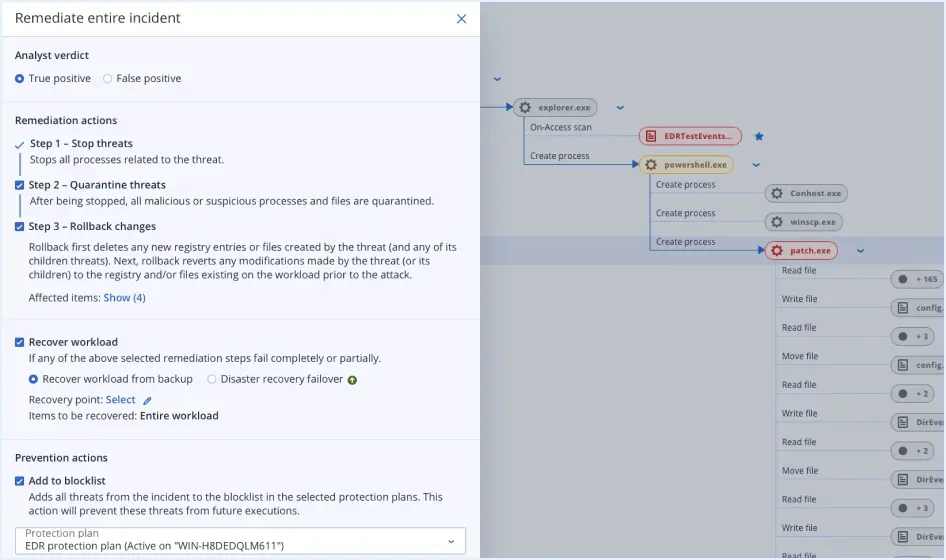
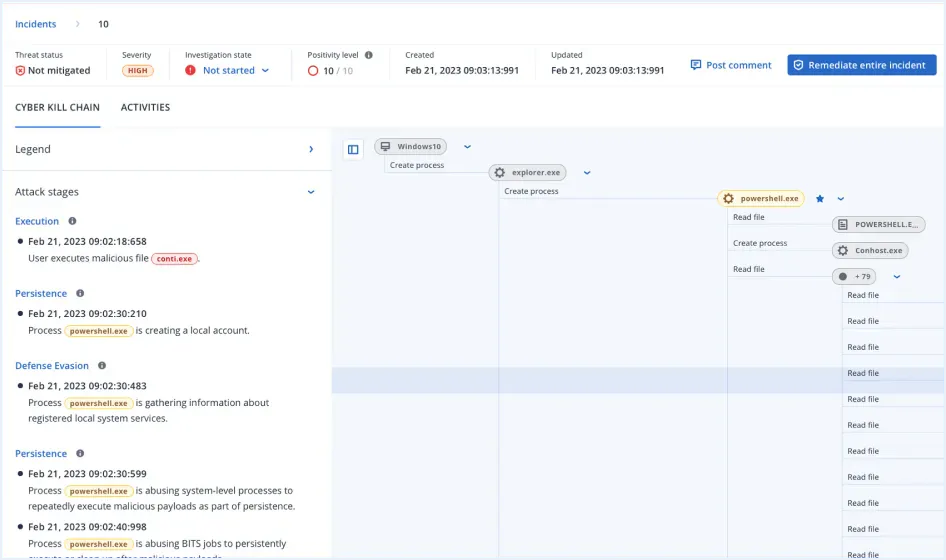
Screenshots: Acronis product interface.
Related Acronis solutions
Acronis Advanced Security + XDR
Unified detection and response across endpoints, email, identity and Microsoft 365.
Acronis Advanced Security + MDR
Have threats monitored and handled 24/7 by an expert security team.
Acronis Advanced Email Security
Stop phishing, BEC and malicious attachments before they reach users.