


Acronis Advanced Security + XDR
Unified detection and response across endpoints, email, identity and Microsoft 365.
What does it do?
An extended detection and response solution that combines security signals from multiple sources to expose complex attacks and handles response on a single platform.
Which needs does it address?
- Reducing the complexity of running many security products
- Quickly understanding how an attack got in and how it spread
- Quickly recovering data after response
Acronis Copilot
GenAI assistant that lets you query incidents in natural language
Automated response playbooks
Ready-made response flows for recurring incidents
MITRE ATT&CK mapping
Automatic interpretation of attack steps
Identity and email integration
Visibility connected with Entra ID and email security
Endpoint isolation
Disconnecting an affected device from the network in one click
Attack-specific rollback
Restoring files and settings affected by the attack
- Scenario 1Investigating email and endpoint traces of a compromised user account together
- Scenario 2Isolating an attack that started with phishing before it spreads
- Scenario 3Reporting the incident timeline for audit
Assessment
We review your current backup, security and licence status.
Deployment
We install agents and policies and carry out the first backups and tests.
Management
Monitoring, incident response and reporting according to your scope.
Security + XDR at a glance
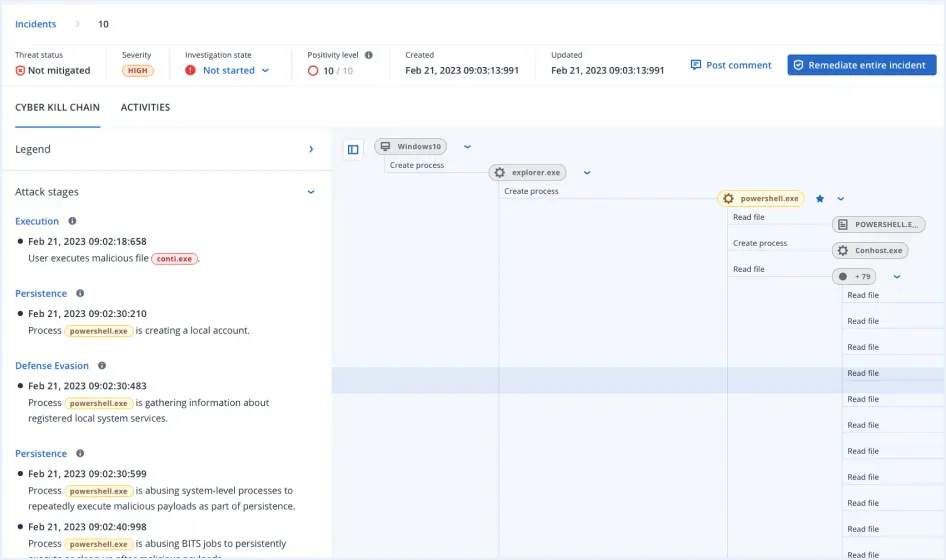
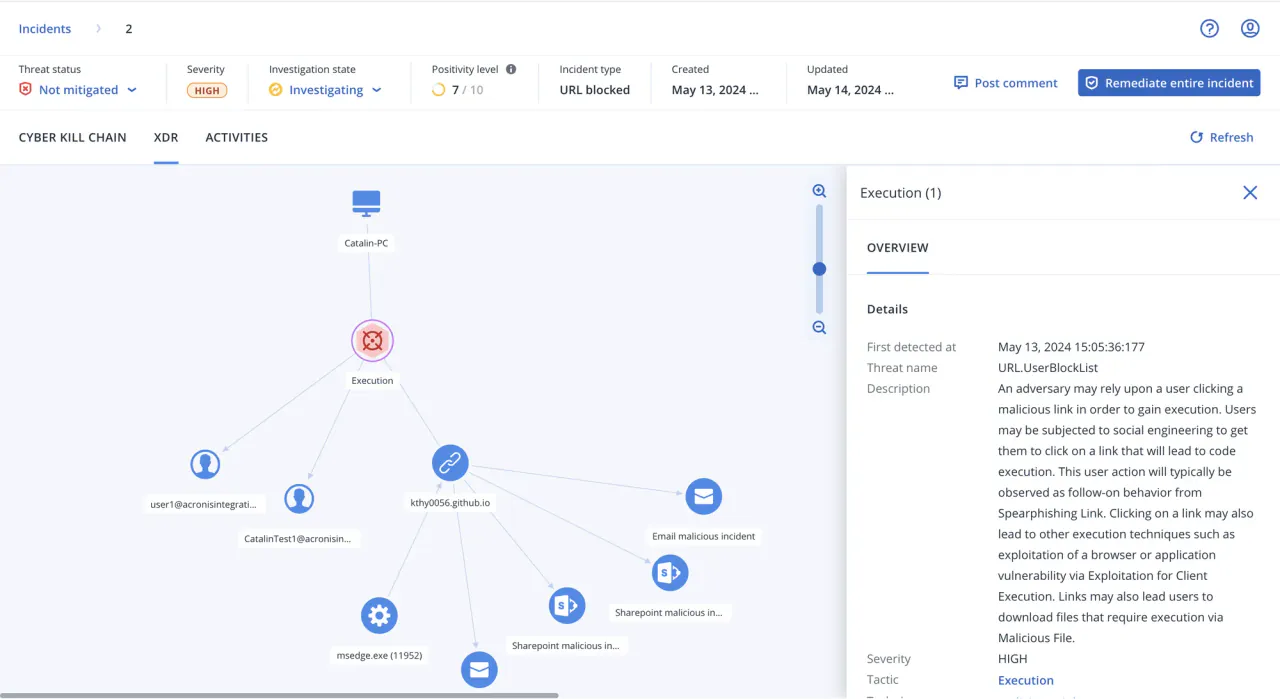
Screenshots: Acronis product interface.